A lost laptop, an unmanaged personal tablet or a shared classroom device left signed in can quickly become more than an everyday IT issue. Schools hold sensitive pupil, staff and safeguarding information, while relying on a growing mix of Windows devices, iPads, Chromebooks, mobile phones and cloud applications. Microsoft Intune for schools gives IT teams a practical way to manage that complexity without making teaching harder.
For schools, colleges and Multi-Academy Trusts, Intune is not simply a tool for installing software remotely. Used well, it forms part of a security-first device strategy: setting expectations before a device reaches a classroom, protecting data wherever it is accessed and giving support teams clearer visibility when something goes wrong.
What Microsoft Intune for Schools Actually Does
Microsoft Intune is Microsoft’s cloud-based endpoint management platform. Authorised IT staff can enrol, configure, secure and support devices from a central location. This includes school-owned Windows laptops, tablets and mobile phones, as well as personal devices where a bring-your-own-device policy suits the organisation.
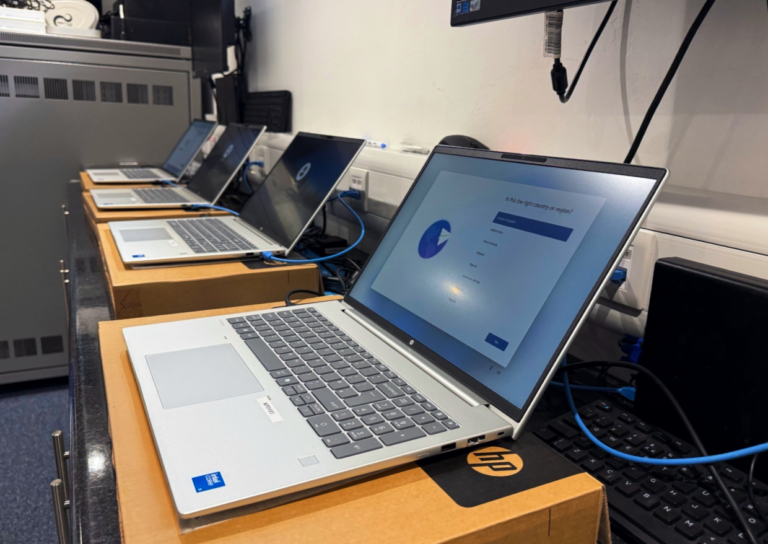
The platform delivers consistency. Rather than preparing each device manually, IT teams can automatically apply approved settings, required applications and security controls. Staff can receive a new laptop, connect it to the internet and sign in, while Intune configures the device for its assigned user with minimal IT involvement. For Trusts managing multiple sites, this approach reduces the inconsistencies that often arise when each school follows its own device build process.
Intune supports device encryption, operating system updates, password and sign-in policies, antivirus management, application deployment and the remote removal of school data. It also integrates closely with Microsoft 365 identity services, allowing schools to make access decisions based on a device’s security status.
However, schools should not apply identical policies to every device. Shared classroom iPads, teacher laptops and finance team mobile phones present different risks and requirements. Intune allows IT teams to create role-specific policies, provided they plan the design carefully.
Where Intune Delivers the Strongest Education Outcomes
The most immediate benefit is often a more reliable device experience. Staff gain access to applications such as Microsoft 365 Apps, web browsers, safeguarding tools, print services and subject-specific software without waiting for technician support. IT teams can also keep devices up to date through scheduled update policies, reducing support requests caused by outdated software or inconsistent configurations.
Security provides another major advantage. Encryption helps protect data if someone loses or steals a device. Compliance policies identify devices that fall below the school’s security standards, such as devices running outdated operating systems, missing encryption or lacking active endpoint protection. Conditional Access policies can then restrict access to Microsoft 365 resources until users resolve those issues.
This capability especially benefits staff who work across multiple sites or from home. Schools can verify both the user’s identity and the device’s security posture before granting access to email, SharePoint or Teams.
For Multi-Academy Trusts, Intune can help balance central governance with local flexibility. Trust leaders can set baseline requirements for encryption, updates, approved applications and administrative access across all schools. Individual schools can still maintain unique device profiles or curriculum applications where operational needs justify them. Effective centralisation strengthens control without forcing every school into a single configuration.
The Decisions to Make Before Deployment
Intune delivers the best results when organisations implement it as part of a clear service and security strategy. Without reviewing the existing environment first, schools risk carrying existing problems into a new management platform.
Start by assessing the device estate. Identify which devices the school owns, shares, supports, plans to replace or no longer considers fit for purpose. Go beyond the laptop register and review operating systems, ownership, user types, locations, encryption status and enrolment compatibility.
Next, define user groups clearly. Teaching staff, support staff, pupils, governors, senior leaders and Trust teams often require different applications, permissions and security controls. Shared devices need particular attention because several users may access the same device throughout the day.
Organisations should also review application compatibility early in the process. Many schools still rely on legacy applications, locally hosted systems or software that requires elevated permissions. While Intune simplifies software deployment, it cannot modernise outdated applications automatically. Some organisations may need phased migrations, application packaging or broader infrastructure changes to achieve their goals.
Finally, review licensing carefully rather than making assumptions. Microsoft licensing determines Intune availability, and some advanced security features require additional licences. A proper assessment should identify existing entitlements, confirm the licences needed to achieve the desired outcomes and determine whether the ongoing investment delivers sufficient security and operational benefits.
A practical approach to implementing Intune
A controlled pilot is preferable to an estate-wide switch. Begin with a representative group of IT staff and willing teaching or administrative users. Test the full experience: initial sign-in, application availability, printing, Wi-Fi access, classroom peripherals, updates, remote support and what happens when a device fails a compliance check.
This pilot should also test the policy design, not just the technology. Overly restrictive controls can disrupt lessons and create workarounds. Policies that are too permissive may leave the school exposed. The right approach depends on the device, the user and the data being accessed. A sixth-form student using a personal laptop for web-based learning presents a different risk profile from a member of staff accessing safeguarding records.
Once the pilot is stable, deployment can be staged by site, year group, department or device type. Communication matters. Staff need to know what will change, what is being installed, whether they need to take action and where to get help. Clear guidance prevents uncertainty being interpreted as a technology failure.
The technical setup should include documented configuration standards, named policy owners and a change-control process. Without this governance, settings can gradually be altered in response to isolated requests until the environment becomes difficult to support. A managed IT partner or co-managed team can provide useful independent oversight here, particularly where a small internal team is already responsible for day-to-day support.
Security controls that need careful handling
The most successful Intune deployments protect people as well as devices. Multi-factor authentication, encryption and timely patching are sensible foundations, but their implementation must account for the school day. A forced restart in the middle of an examination or lesson is not a good outcome, even if the update itself is necessary.
Set update rings that provide time for testing before broad release, with clear deadlines for critical security patches. Define an emergency process for serious vulnerabilities, including who can approve accelerated updates and how affected users will be informed.
Administrative privilege is another common weakness. Staff may request local administrator rights to install software or resolve a one-off issue. Granting broad permanent access is rarely the safest answer. Consider controlled application deployment, time-limited elevation where appropriate and a clear route for requesting new software. These measures reduce risk without turning every request into a prolonged support issue.
For personal devices, distinguish between managing the entire device and protecting school data within approved applications. Full device management may be appropriate in limited circumstances, but it can be intrusive for staff-owned phones. Application protection policies can often secure Microsoft 365 data by requiring a PIN, limiting copy-and-paste and allowing work data to be removed without affecting personal photos or files. The policy must be transparent, proportionate and aligned with the school’s data protection responsibilities.
Intune is an operational commitment, not a one-off project
After deployment, Intune needs active ownership. New applications must be assessed and packaged, old devices retired, policies reviewed, compliance alerts investigated and reporting used to identify gaps. A device management platform is only as effective as the processes around it.
Regular reporting should answer practical leadership questions: which devices are unsupported, which are missing critical updates, where encryption is absent, whether required applications are installed and whether the estate is moving towards or away from its agreed standard. This turns endpoint management into useful operational information rather than a technical dashboard viewed only when there is a problem.
Schools across Cambridge, Cambridgeshire and the wider South East often face the same challenge: limited internal capacity alongside a growing responsibility to protect users, data and learning continuity. Ask IT Solutions can support schools and Trusts with the planning, rollout and ongoing management required to make Intune part of a dependable wider IT service.
The best next step is not to ask whether Intune has every feature a school might need. It is to identify the devices, users and risks that currently create the greatest exposure, then build a manageable standard that improves security without getting in the way of education.